The advisor
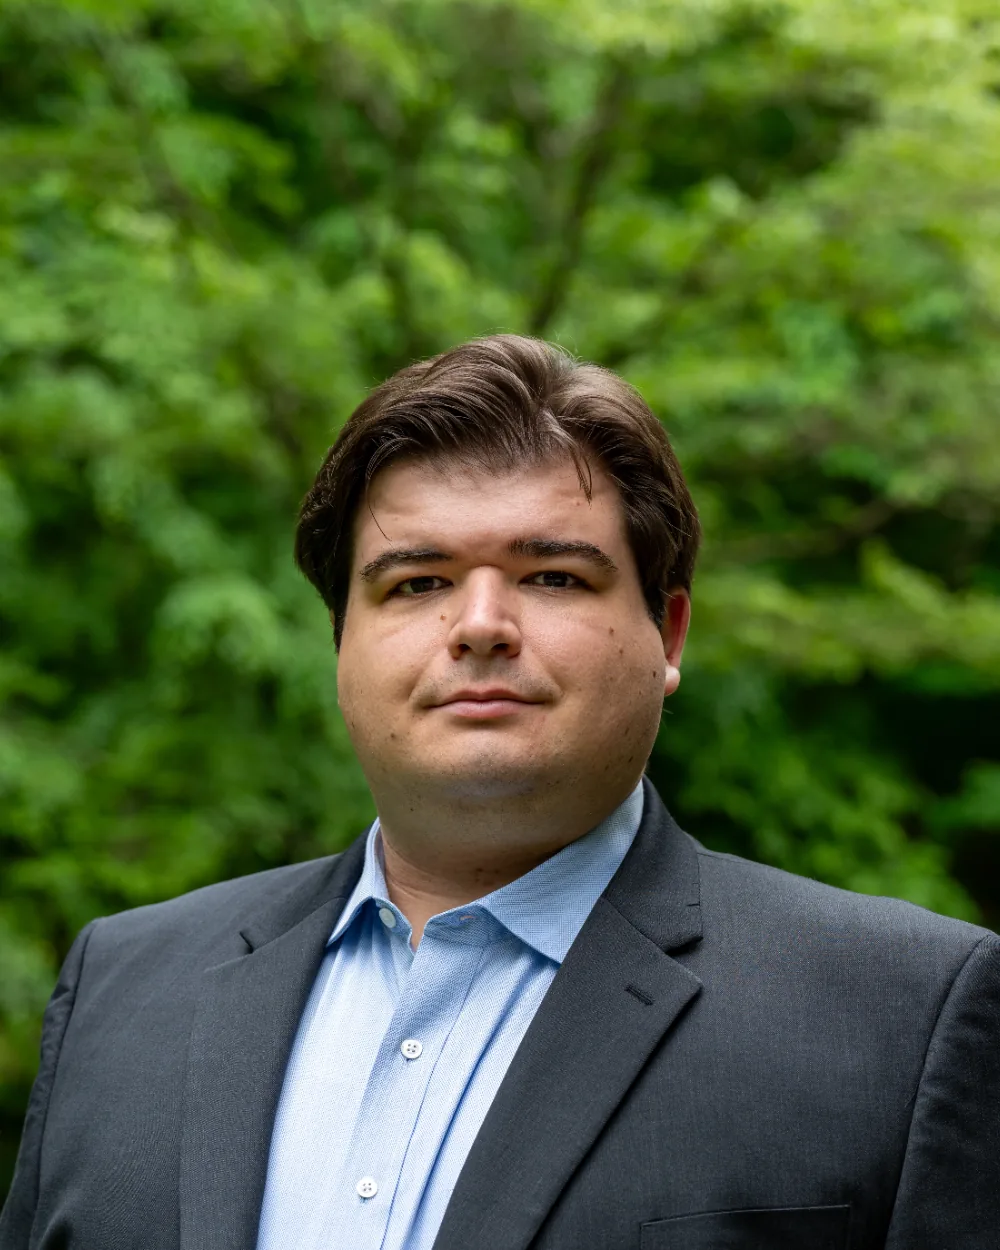
Alex Sellers
Blackhole Cyberstrategy is led by Alex Sellers, a security advisor working on strategy, governance, risk prioritization, and programs leaders can understand and sustain — AI governance, SOC 2 and ISO readiness, application and cloud security, vulnerability reduction, tabletop exercises, and executive security planning.
When scope calls for it, vetted senior practitioners join the engagement under the same terms, and Alex remains your point of contact — on the fit call, in the work, and in front of your leadership. Trusted open-source and vetted vendor tools are used where they earn their place.
Where the work concentrates
AI governance — adoption policies, NIST AI RMF-based assessments, and tool approvals leadership can defend to customers and counsel
SOC 2, ISO 27001, and ISO 42001 — guiding you to audit or attestation readiness without building a paperwork factory. Not an auditor; you choose the audit firm
Application and cloud security — risk-ranked, sequenced against engineering capacity. Independent testing firms are recommended and coordinated when testing is warranted; they contract with you directly
Vulnerability reduction — fewer findings carried quarter to quarter, with owners and SLAs. The pace depends on your engineering capacity, which the plan is sequenced against
Tabletop exercises — incident response and disaster recovery rehearsals that find the gaps in roles, backups, and communications before an incident does
First security hire and team build — the business case, role, interview loop, and 30-60-90 plan, and the Champions program that extends coverage without headcount
Vendor and SaaS risk — repeatable third-party reviews that turn tool adoption into documented decisions
Executive security planning — briefs, budgets, and executive and customer-ready reporting that hold up
Boundaries
Fractional CISO responsibilities begin with an explicit mandate: defined authority, reporting expectations, and accountable outcomes. Outside such a mandate, the role is advisory. Security exists to protect the business so it can sell, ship, and grow; the job is to enable revenue, not to say no and slow good work down. Regulated finance, healthcare, government, and safety-critical operations get a referral, not a stretch.
Twenty minutes, one decision.
Bring the decision in front of you. Leave with a straight answer — including if the answer is no.