External pressure
A customer, audit, insurer, or investor is asking questions the business cannot answer with confidence.
Security advisor · fractional CISO
A blackhole route drops hostile traffic before it reaches anything that matters. Same idea, applied to security leadership: fewer open questions reaching your board, a risk-ranked plan your team can actually fund and execute.
Security exists to protect the business so it can sell, ship, and grow. The job is to enable revenue, not to say no and slow good work down.
Built for US B2B and public-sector organizations, roughly 50–500 people, that need senior security leadership before they can justify a full-time CISO.
Why the name
blackhole (networking) — a route that quietly discards hostile traffic. Nothing malicious gets through, and nothing noisy gets out.
That is the job of the engagement: absorb the ambiguity, the vendor noise, and the half-finished findings, and hand leadership back a small number of decisions worth making.
When to engage
Senior guidance earns its cost when the business needs a decision, an accountable owner, or a plan it can defend.
A customer, audit, insurer, or investor is asking questions the business cannot answer with confidence.
Cloud, identity, application, or AI adoption is moving faster than anyone's mandate to govern it.
Work keeps accumulating, but there is no risk-ranked order the team can fund, staff, and finish.
A raise, an enterprise deal, an audit, or a board meeting needs a credible security narrative before it lands.
Ways to engage
Each level states what I own, what your team keeps, and who it is not for — so you can rule two of them out before we ever speak.
Pricing is discussed on the fit call, once scope is clear. No packages, no retainer you cannot exit.
Not sure? Take the 2-minute fit checkFocused engagements
Each of these stands on its own, or slots into a Sprint or a retained cadence. Fixed scope, a named deliverable, and a reason it is worth doing now.
AI governance
Acceptable-use policy, NIST AI RMF-based risk assessment, tool approval paths, and employee guidance, so adoption moves without exposing data.
Exercises
A rehearsed team decides better under pressure. The exercise finds gaps in roles, backups, and communications before an incident does.
Third-party risk
Every new tool is a new place your data lives. A repeatable review turns vendor risk into a documented decision procurement can act on.
Team
Role definition, interview loop, scoring model, and 30-60-90 plan, so your first hire lands with a mandate instead of a backlog.
Culture
Coverage without security headcount: engineers who own security where the work happens, with ongoing support after launch.
Awareness
Training run as an operation: recurring communications, phishing response, and aggregate reporting leadership can act on.
Governance
Policies people can find, read, and follow, structured so auditors and customers get answers without a scramble.
Risk
Each risk tied to evidence, an owner, an action, and an indicator, so leadership sets risk appetite from facts.
Access
Remote access and private-application exposure turned into a prioritized, fundable proposal with rollout risks named.
Productivity suite
Identity, mail authentication, sharing, device, and admin settings reviewed against current baselines, with a sequenced hardening list.
Cloud
AWS and GCP (Azure on request): IAM, encryption, logging, and public exposure ranked by business impact and sequenced against engineering capacity.
Assurance
Guidance to audit or attestation readiness: control ownership, evidence operations, policy rollout, and auditor liaison. Not an audit.
Scoped and priced on the fit call. Trusted open-source and vetted vendor tools are used where they earn their place.
What each one delivers, and whyApproach
Four steps, in order, every time. You will always know which one we are in.
Your business, your obligations, and what a good outcome looks like to leadership.
Controls, gaps, and exposure — measured against the decisions you actually face. Evidence-based: interviews, documentation, and read-only review of what you choose to show. Tooling only when scope calls for it.
A short, funded sequence — with the things we are deliberately not doing named out loud.
Review, coaching, vendor coordination, and reporting that keep the plan credible after the excitement fades.
“A dedicated security professional is not always what an organization needs. What it needs is guidance and a roadmap it can implement while it keeps building excellence, without slowing down.”
What you hold at day 30
Every engagement produces these, starting in its first month. They are yours to keep, reuse, and hand to whoever comes next.
DOC 01
Where you are, where the business needs you to be, and the gap in between.
DOC 02
Each risk tied to exposure, urgency, a named owner, and a decision path.
DOC 03
Options and tradeoffs a board can read in ten minutes and act on.
DOC 04
Sequenced against real capacity, with accountable next steps.
The advisor
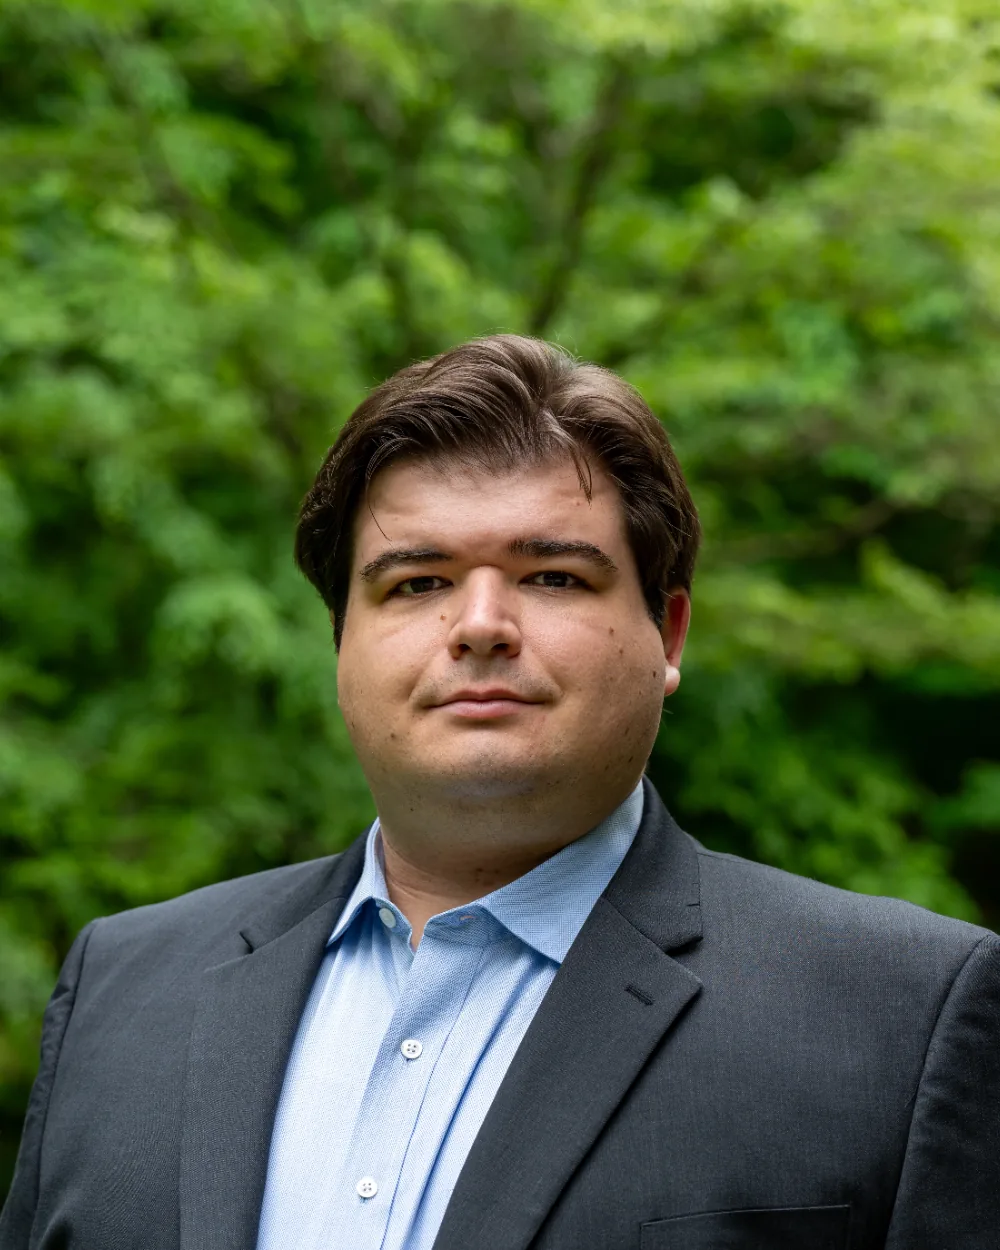
Alex Sellers CISSP, CISM
Blackhole Cyberstrategy is led by Alex Sellers, a security advisor working on strategy, governance, risk prioritization, and programs leaders can understand and sustain — AI governance, SOC 2 and ISO readiness, application and cloud security, vulnerability reduction, tabletop exercises, and executive security planning.
When scope calls for it, vetted senior practitioners join the engagement under the same terms, and Alex remains your point of contact. Trusted open-source and vetted vendor tools are used where they earn their place.
Fractional CISO responsibilities begin with an explicit mandate: defined authority, reporting expectations, and accountable outcomes.
More about AlexNext step
Bring the security decision or business milestone you are preparing for. You will leave with a straight answer about whether this is worth continuing — including if the answer is no.
Please do not send credentials, logs, reports, diagrams, or incident evidence — not now, and not by email.
What happens
Or email [email protected]